US NAIC 668 – Insurance Data Security Model Law

Operationalize US NAIC 668 compliance with the most comprehensive PrivacyOps platform

Last Updated on May 13, 2024

Schedule Your
Personal Demo

Learn how you can leverage Securiti’s DataAI Command Platform to address data security, privacy, governance, and compliance.

See a demo
Schedule your demo today

The "Insurance Data Security Model Law," or NAIC Model Regulation 668, was developed by the National Association of Insurance Commissioners (NAIC) in the United States. This model law establishes cybersecurity standards and requirements for insurance companies to protect nonpublic information's confidentiality, integrity, and availability.

The NAIC Model 668 applies to licensees who are defined as persons licensed, authorized to operate, or registered, or required to be licensed, authorized, or registered pursuant to the insurance laws of the state but shall not include a purchasing group or risk retention group chartered and licensed in a state other than this state or a licensee that is acting as an assuming insurer that is domiciled in another state or jurisdiction.

The NAIC Model Regulation 668 acts as a model or template that other U.S. states can use as a starting point for developing their own regulatory frameworks. As a result, each state may vary in terms of specific requirements and details of the regulation.

The NAIC Model Regulation 668 is one of the four primary model NAIC Laws. The other three laws are the model Insurance Information and Privacy Protection Act (#670), the model Privacy of Consumer Financial and Health Information Regulation (#672), and the model Standards for Safeguarding Customer Information Regulation (#673). These standards govern the collection, use, and disclosure of information in relation to insurance transactions made by insurance institutions, agents, or insurance support organizations. The NAIC Model Regulation 668 imposes cybersecurity obligations concerning personally identifiable information.

The NAIC Model 668 has been adopted by several US states, including Alabama, Connecticut, Delaware, Indiana, Iowa, Louisiana, Maine, Maryland, Michigan, Minnesota, Mississippi, New Hampshire, New York, North Dakota, South Carolina, Tennessee, Virginia, Wisconsin, and Ohio.

The Solution

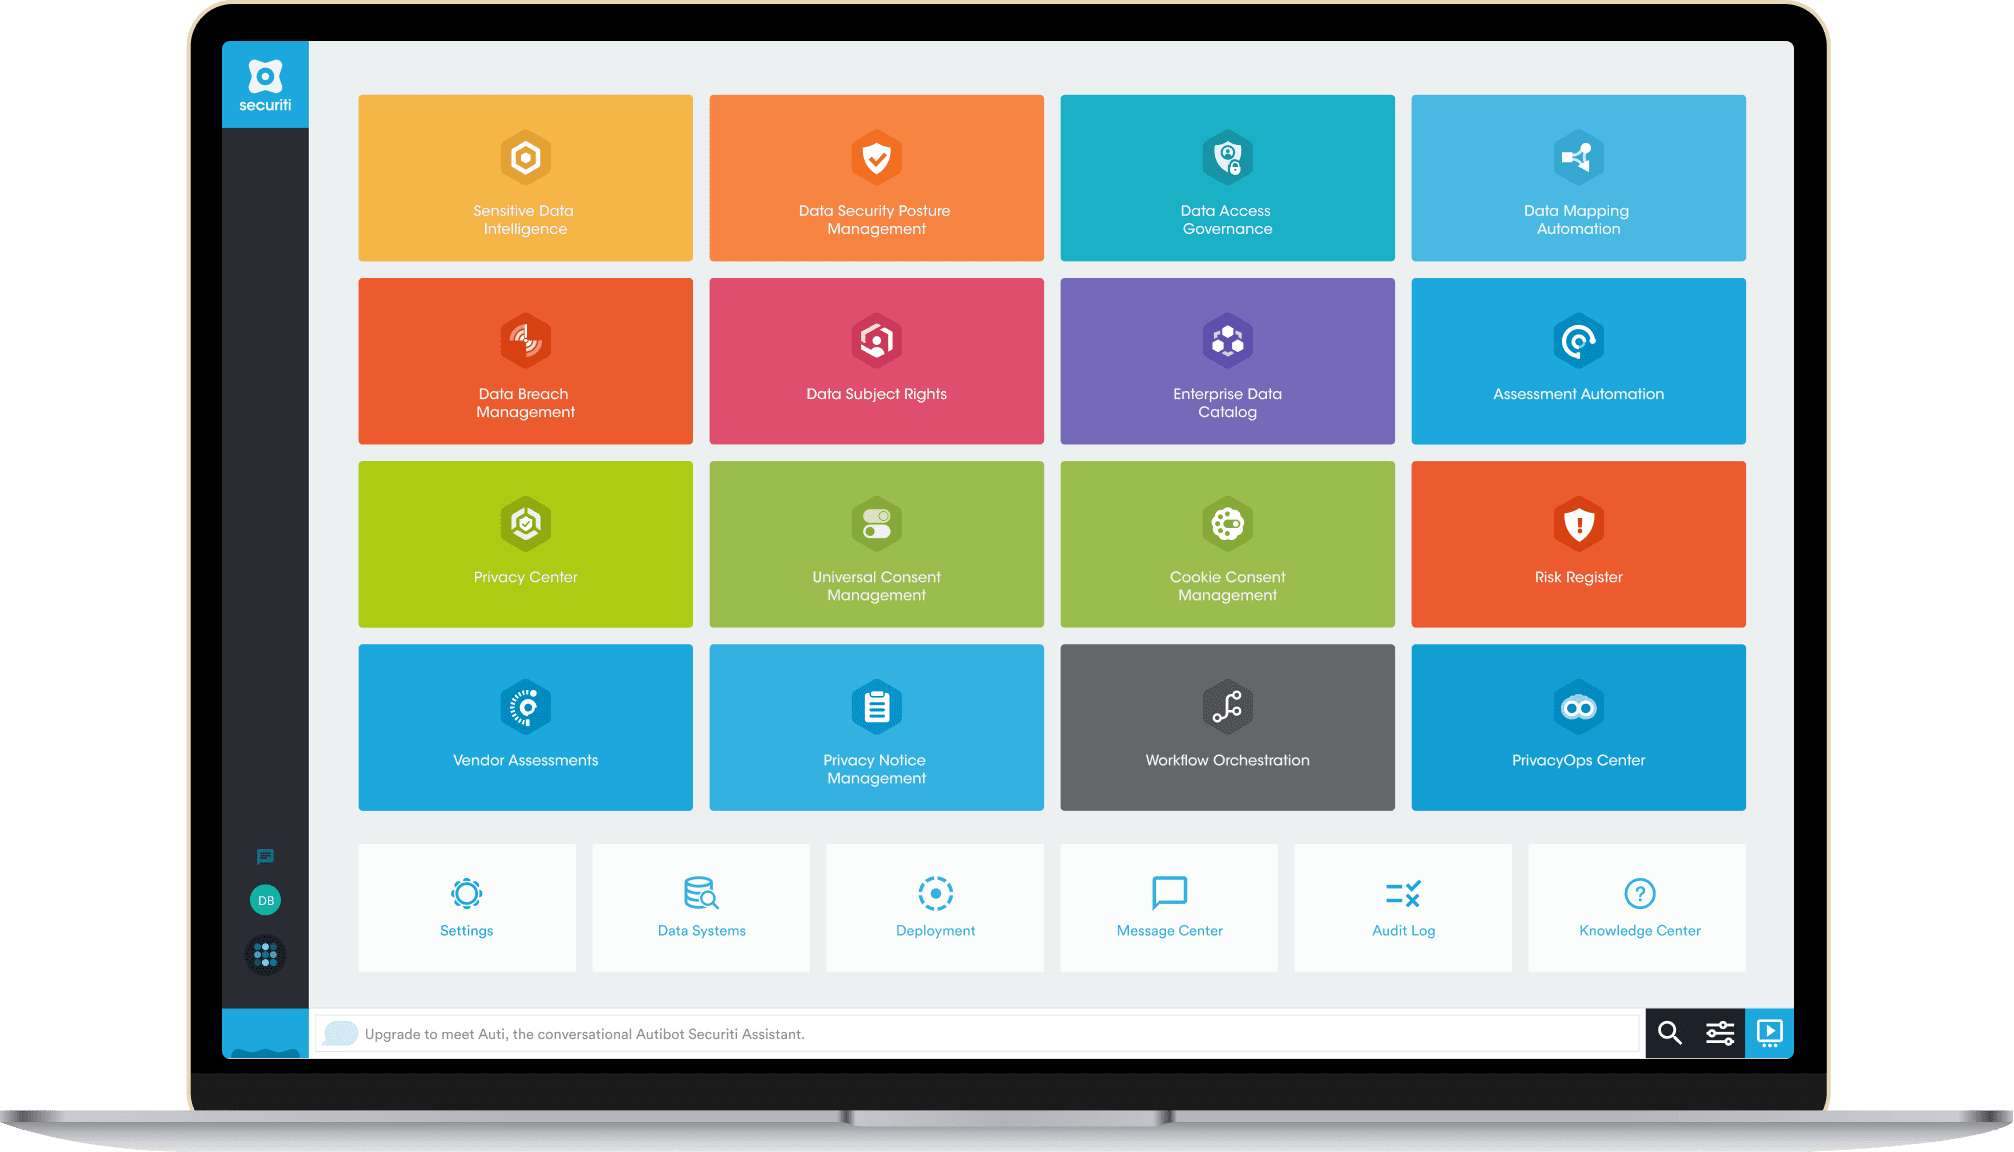
Securiti enables organizations to comply with US NAIC 668 – Insurance Data Security Model Law through AI-driven PI data discovery, DSR automation, documented accountability, enhanced visibility into data processing activities, and AI-driven process automation.

Securiti supports enterprises' journey toward compliance with US NAIC 668 – Insurance Data Security Model Law through automation, enhanced data visibility, and identity linking.
 

US California CCPA

Request a demo to learn how Securiti can aid you and your organization's compliance efforts today.


Assess US NAIC 668 Readiness

US NAIC 668 Section: 2

Utilize Securiti's collaborative readiness assessment template to assess your organization's compliance with NAIC 668 requirements, assess compliance gaps, and mitigate risks. Seamlessly expand assessment capabilities across your vendor ecosystem to maintain compliance against this standard.

New South Wales Assess GDPR readiness
New South Wales breach response notification

Implement Automated Breach Management and Notifications

US NAIC 668 Sections: 4(H), 6

Securiti's Breach Management enables organizations to create an incident response plan to respond effectively to security incidents that compromise the confidentiality, integrity, or availability of information. It assists organizations in making breach notifications to relevant stakeholders as per the requirements of the industry law and applicable laws.

Assess Breach Risk Severity

US NAIC 668 Section: 5

Securiti's Assessment Automation allows organizations to assess the nature and scope of security incidents with the help of breach and breach risk severity assessments. The assessments facilitate organizations to identify what information has been breached, restore security, take reasonable measures in order to protect any unauthorized acquisition or disclosure of information and identify which parties are required to be notified of the breach.

New South Wales PPIPA
New South Wales vendor risk management

Automate Risk Assessment and Vendor Risk Management

US NAIC 668 Sections: 4(C), 4(F)

Securiti's Assessment Automation enables organizations to assess safeguards in place for protecting data and associated risks and assess and mitigate third-party risks.

Assess Data Security Posture

US NAIC 668 Sections: 4(C)(5), 4(D)

Securiti's Data Security Posture Management module allows organizations to identify and implement appropriate security controls.

New South Wales Data Security Posture assessment

Key Facts about US NAIC 668 – Insurance Data Security Model Law

1

Data Security Program: Insurance companies must create, implement, and maintain a thorough written information security program to protect nonpublic information. This program should include administrative, technical, and physical safeguards.

2

Risk Assessment: Insurers must regularly review their risks to identify potential vulnerabilities and threats to nonpublic information by conducting risk assessments. The Information Security Program must be designed to mitigate identified risks as per the sensitivity of the non-public information. Third-party service providers are required to be included in the risk management process.

3

Security measures: Access controls, encryption, multi-factor authentication, regular testing, audit trails, protection against breaches, and secure disposal of information are some of the security measures highlighted in the NAIC 668 standard.

4

Incident Response Plan: To address and quickly minimize the effects of cybersecurity occurrences, insurance companies must have an incident response plan in place.

5

Employee Training: Employees must receive appropriate cybersecurity awareness training.

6

Notification of Cybersecurity Events: The licensee must notify the Commissioner and consumers in the case of a cybersecurity event. The notification to the Commissioner must be made as promptly as possible but no later than 72 hours from a determination that a cybersecurity event has occurred.

7

Annual Certification: Insurance regulators in each state may require insurers to certify compliance with the regulation annually.

8

Records Retention: After the date of each cybersecurity event, the Licensee must keep records pertaining to those events for at least five years. The Commissioner may request those data at any time.

Analyze this article with AI

Prompts open in third-party AI tools.
IDC MarketScape

Securiti named a Leader in the IDC MarketScape for Data Privacy Compliance Software

Read the Report
Videos
View More
Rehan Jalil, Veeam on Agent Commander : theCUBE + NYSE Wired: Cyber Security Leaders
Following Veeam’s acquisition of Securiti, the launch of Agent Commander marks an important step toward helping enterprises adopt AI agents with greater confidence. In...
View More
Mitigating OWASP Top 10 for LLM Applications 2025
Generative AI (GenAI) has transformed how enterprises operate, scale, and grow. There’s an AI application for every purpose, from increasing employee productivity to streamlining...
View More
Top 6 DSPM Use Cases
With the advent of Generative AI (GenAI), data has become more dynamic. New data is generated faster than ever, transmitted to various systems, applications,...
View More
Colorado Privacy Act (CPA)
What is the Colorado Privacy Act? The CPA is a comprehensive privacy law signed on July 7, 2021. It established new standards for personal...
View More
Securiti for Copilot in SaaS
Accelerate Copilot Adoption Securely & Confidently Organizations are eager to adopt Microsoft 365 Copilot for increased productivity and efficiency. However, security concerns like data...
View More
Top 10 Considerations for Safely Using Unstructured Data with GenAI
A staggering 90% of an organization's data is unstructured. This data is rapidly being used to fuel GenAI applications like chatbots and AI search....
View More
Gencore AI: Building Safe, Enterprise-grade AI Systems in Minutes
As enterprises adopt generative AI, data and AI teams face numerous hurdles: securely connecting unstructured and structured data sources, maintaining proper controls and governance,...
View More
Navigating CPRA: Key Insights for Businesses
What is CPRA? The California Privacy Rights Act (CPRA) is California's state legislation aimed at protecting residents' digital privacy. It became effective on January...
View More
Navigating the Shift: Transitioning to PCI DSS v4.0
What is PCI DSS? PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards to ensure safe processing, storage, and...
View More
Securing Data+AI : Playbook for Trust, Risk, and Security Management (TRiSM)
AI's growing security risks have 48% of global CISOs alarmed. Join this keynote to learn about a practical playbook for enabling AI Trust, Risk,...

Spotlight Talks

Spotlight 00:00
AI Agents Unleashed? The Future of Identity & Data Access Security
Watch Now View
Spotlight 00:00
IDC Research: Why Data, AI, Identity and Access Security Must Come Together
Watch Now View
Spotlight 59:11
Data Controls for AI: Findings from the 2026 GigaOm DSPM Research
Watch Now View
Spotlight 1:02:06
Consent by proxy: When AI agents start deciding for us
Watch Now View
Spotlight 1:00:41
Future-Proofing for the Privacy Professional
Watch Now View
Spotlight 50:52
From Data to Deployment: Safeguarding Enterprise AI with Security and Governance
Watch Now View
Spotlight 11:29
Not Hype — Dye & Durham’s Analytics Head Shows What AI at Work Really Looks Like
Watch Now View
Spotlight 11:18
Rewiring Real Estate Finance — How Walker & Dunlop Is Giving Its $135B Portfolio a Data-First Refresh
Watch Now View
Spotlight
Choosing the Right DSPM: An Industry Analyst’s Perspective
Watch Now View
Spotlight 13:38
Accelerating Miracles — How Sanofi is Embedding AI to Significantly Reduce Drug Development Timelines
Sanofi Thumbnail
Watch Now View
Latest
KSA PDPL in 2026 View More
KSA PDPL in 2026: What Organizations Need to Know Now
KSA's Personal Data Protection Law (PDPL) has been fully enforceable since 14th September 2024. Over the past two years, organizations have been navigating overlapping...
EU Digital Sovereignty View More
EU Digital Sovereignty is Moving from Policy to Procurement: What Organizations Need to Know
Digital sovereignty in Europe is moving from policy ambition toward something much more concrete: a framework that can determine how cloud services are assessed,...
View More
What Is Unstructured Data Discovery? A Practical Guide
Unstructured data discovery finds sensitive data in files, chats, and cloud storage. Securiti explains how it works, common challenges, and best practices.
Data Anonymization View More
What Is Data Anonymization
What is data anonymization? Securiti’s latest blog explains how it works, key techniques, and how it differs from pseudonymization. Read to learn more.
Saudi PDPL Compliance Toolkit View More
Saudi PDPL Compliance Toolkit
Turn Saudi PDPL requirements into action with practical checklists, a maturity self-assessment, and a 90-day plan for privacy and compliance leaders.
From Compliance to Continuous Assurance View More
From Compliance to Continuous Assurance: The Next Era of Saudi Data Protection
PDPL compliance didn’t end with the deadline. Learn how to comply with SDAIA enforcement requirements, govern cross-border transfers, and prepare your data for AI.
Data Minimization, Data Minimization for AI, Safe AI, AI Readiness, ROT Data, AI Governance, Data Governance, Data and AI Security, AI Risk Management, Sensitive Data View More
Minimize Before You Scale
Discover why redundant, obsolete, and trivial (ROT) data raises AI-era risks and how to minimize them. Explore practical fixes and business outcomes.
The PDPL Operational Lifecycle View More
The PDPL Operational Lifecycle
Find it. Fix it. Prove it. Repeat. Explore the 10-stage PDPL operational lifecycle, key deadlines, and the evidence regulators expect.
View More
Take the Data Risk Out of AI
Learn how to prepare enterprise data for safe Gemini Enterprise adoption with upstream governance, sensitive data discovery, and pre-index policy controls.
View More
Navigating HITRUST: A Guide to Certification
Securiti's eBook is a practical guide to HITRUST certification, covering everything from choosing i1 vs r2 and scope systems to managing CAPs & planning...
What's
New