KSA Essential Cybersecurity Controls (ECC – 1: 2018)

Last Updated on August 6, 2024

Schedule Your
Personal Demo

Learn how you can leverage Securiti’s DataAI Command Platform to address data security, privacy, governance, and compliance.

See a demo
Schedule your demo today

The Kingdom of Saudi Arabia's Essential Cybersecurity Controls (ECC-1: 2018) provides a structured framework aimed at enhancing the cybersecurity posture of organizations operating within the KSA. This comprehensive set of guidelines covers various aspects of cybersecurity, including governance, risk management, compliance, technical controls, and incident response.

The ECC framework helps organizations protect their information assets and maintain their systems' integrity, confidentiality, and availability by establishing clear roles and responsibilities, creating strong risk management plans, and complying with relevant laws and standards.

The ECC-1: 2018 also highlights the need for regular upgrades, continuous monitoring, and ensuring cybersecurity awareness. It emphasizes the physical security of information systems and requires the use of technological controls such as encryption, network security measures, and access management.

The solution

Securiti enables organizations to comply with KSA’s Essential Cybersecurity Controls (ECC-1: 2018) through AI-driven PI data discovery, DSR automation, documented accountability, enhanced visibility into data processing activities, and AI-driven process automation.

ADHICS Compliance Solution

Securiti supports enterprises' journey toward compliance with KSA’s Essential Cybersecurity Controls (ECC-1: 2018) through automation, enhanced data visibility, and identity linking.


Compliance Management

1-1 Cybersecurity Strategy

To ensure that cybersecurity plans, goals, initiatives, and projects are enabling compliance with related laws and regulations.

ADHICS dsr portal
ADHICS dsr handling

Data Security Posture Management, Compliance Management

1-2 Cybersecurity Management

To ensure that the head of the organization or his/her delegate (defined as an Authorizing Official) supports the implementation and management of cybersecurity programs and objectives within the organization as per related laws and regulations.

Compliance Management, Policy & Notice Management

1-3 Cybersecurity Policies and Procedures

To ensure that the organization documents, communicates, and complies with cybersecurity requirements in accordance with relevant laws and regulations and organizational requirements.

ADHICS data access request
ADHICS personal data monitoring tracking

Compliance Management, Policy & Notice Management

1-4 Cybersecurity Roles and Responsibilities

To ensure that roles and responsibilities are defined for all parties participating in implementing the cybersecurity controls within the organization.

Data Security Posture Management, Data Access Governance, Assessment Automation

1-5 Cybersecurity Risk Management

To ensure the management of cybersecurity risks using a methodological approach to protect the organization’s information and technology assets as per organizational policies and procedures and related laws and regulations.

ADHICS personal information data linking
ADHICS Readiness Assessment

Compliance Management, Assessment Automation

1-6 Cybersecurity in Information and Technology Project Management

To ensure that cybersecurity requirements are included in project management methodology and procedures, protecting the confidentiality, integrity, and availability of information and technology assets according to the organization’s policies and procedures and related laws and regulations.

Compliance Management, Assessment Automation

1-7 Compliance with Cybersecurity Standards, Laws and Regulations

To ensure that the organization’s cybersecurity program complies with related laws and regulations.

ADHICS Data Flow Mapping
ADHICS Vendor Risk Management

Assessment Automation, Compliance Management, Data Security Posture Management

1-8 Periodical Cybersecurity Review and Audit

To ensure that cybersecurity controls are implemented and in compliance with organizational policies and procedures, as well as related national and international laws, regulations and agreements.

Compliance Management

1-9 Cybersecurity in Human Resources

To ensure that cybersecurity risks and requirements related to personnel (employees and contractors) are managed efficiently prior to employment, during employment and after termination/separation as per organizational policies and procedures and related laws and regulations.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management

1-10 Cybersecurity Awareness and Training Program

To ensure that personnel are aware of their cybersecurity responsibilities and have essential cybersecurity awareness. It is also to ensure that personnel are given the required cybersecurity skills, training and credentials needed to accomplish their cybersecurity responsibilities and protect the organization’s information and technology assets.

Asset and Data Discovery, Sensitive Data Intelligence, Data Mapping

2-1 Asset Management

To ensure that the organization has an accurate and detailed inventory of information and technology assets to support its cybersecurity and operational requirements and maintain their confidentiality, integrity, and availability.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management, Data Access Governance

2-2 Identity and Access Management

To ensure secure and restricted logical access to information and technology assets, prevent unauthorized access, and allow only authorized access for users necessary to accomplish assigned tasks.

Data Security Posture Management, Data Access Intelligence & Governance

2-3 Information System and Information Processing Facilities Protection

To ensure the protection of information systems and information processing facilities (including workstations and infrastructures) against cyber risks.

ADHICS breach response notification
ADHICS Vendor Risk Management

Data Security Posture Management, Compliance Management

2-4 Email Protection

To ensure the protection of the organization’s email service from cyber risks.

Data Security Posture Management, Data Access Intelligence & Governance, Compliance Management

2-5 Networks Security Management

To ensure the protection of an organization’s network from cyber risks.

ADHICS breach response notification
ADHICS Vendor Risk Management

Data Security Posture Management, Compliance Management

2-6 Mobile Devices Security

To ensure the protection of mobile devices (including laptops, smartphones, and tablets) from cyber risks and the secure handling of the organization’s information (including sensitive information) while utilizing the Bring Your Own Device (BYOD) policy.

Data Privacy Management

2-7 Data and Information Protection

To ensure the confidentiality, integrity, and availability of the organization’s data and information as per organizational policies and procedures and related laws and regulations.

ADHICS breach response notification
ADHICS Vendor Risk Management

Data Security Posture Management

2-8 Cryptography

To ensure the proper and efficient use of cryptography to protect information assets as per organizational policies and procedures, and related laws and regulations.

Compliance Management, Data Security Posture Management

2-9 Backup and Recovery Management

To ensure the protection of the organization’s data and information, including information systems and software configurations, from cyber risks as per organizational policies and procedures and related laws and regulations.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management, Data Security Posture Management

2-10 Vulnerabilities Management

To ensure timely detection and effective remediation of technical vulnerabilities, preventing or minimizing the probability of exploiting these vulnerabilities to launch cyber attacks against the organization.

Compliance Management, Data Security Posture Management

2-11 Penetration Testing

To assess and evaluate the efficiency of the organization’s cybersecurity defense capabilities through simulated cyber-attacks to discover unknown weaknesses within the technical infrastructure that may lead to a cyber breach.

ADHICS breach response notification
ADHICS Vendor Risk Management

Incident Management, Data Access Intelligence, Data Security Posture Management, Compliance Management

2-12 Cybersecurity Event Logs and Monitoring Management

To ensure timely collection, analysis and monitoring of cybersecurity events for early detection of potential cyber-attacks in order to prevent or minimize the negative impacts on the organization’s operations.

Incident Management

2-13 Cybersecurity Incident and Threat Management

To ensure timely identification, detection, effective management, and handling of cybersecurity incidents and threats to prevent or minimize negative impacts on the organization’s operation, taking into consideration Royal Decree number 37140, dated 14/8/1438H.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management

2-14 Physical Security

To ensure the protection of information and technology assets from unauthorized physical access, loss, theft, and damage.

Compliance Management

2-15 Web Application Security

To ensure the protection of external web applications against cyber risks.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management

3-1 Cybersecurity Resilience Aspects of Business Continuity Management (BCM)

To ensure the organization’s business continuity management includes the cybersecurity resiliency requirements and to remediate and minimize the impacts on systems, information processing facilities and critical e-services from disasters caused by cybersecurity incidents.

Vendor Risk Assessment, Compliance Management, Data Security Posture Management

4-1 Third-Party Cybersecurity

To ensure the protection of assets against cybersecurity risks related to third parties, including outsourcing and managed services, as per organizational policies and procedures and related laws and regulations.

ADHICS breach response notification
ADHICS Vendor Risk Management

Compliance Management, Data Security Posture Management, Assessment Automation

4-2 Cloud Computing and Hosting Cybersecurity

To ensure the proper and efficient remediation of cyber risks and the implementation of cybersecurity requirements related to hosting and cloud computing as per organizational policies and procedures and related laws and regulations. It is also to ensure the protection of the organization’s information and technology assets hosted on the cloud or processed/managed by third parties.

Automate KSA ECC Compliance with Securiti

1

Securiti is the pioneer of the DataAI Command Platform, a centralized platform that enables the safe use of data and GenAI. It provides unified data intelligence, controls, and orchestration across hybrid multicloud environments. Large global enterprises rely on Securiti's DataAI Command Platform for data security, privacy, governance, and compliance. 

2

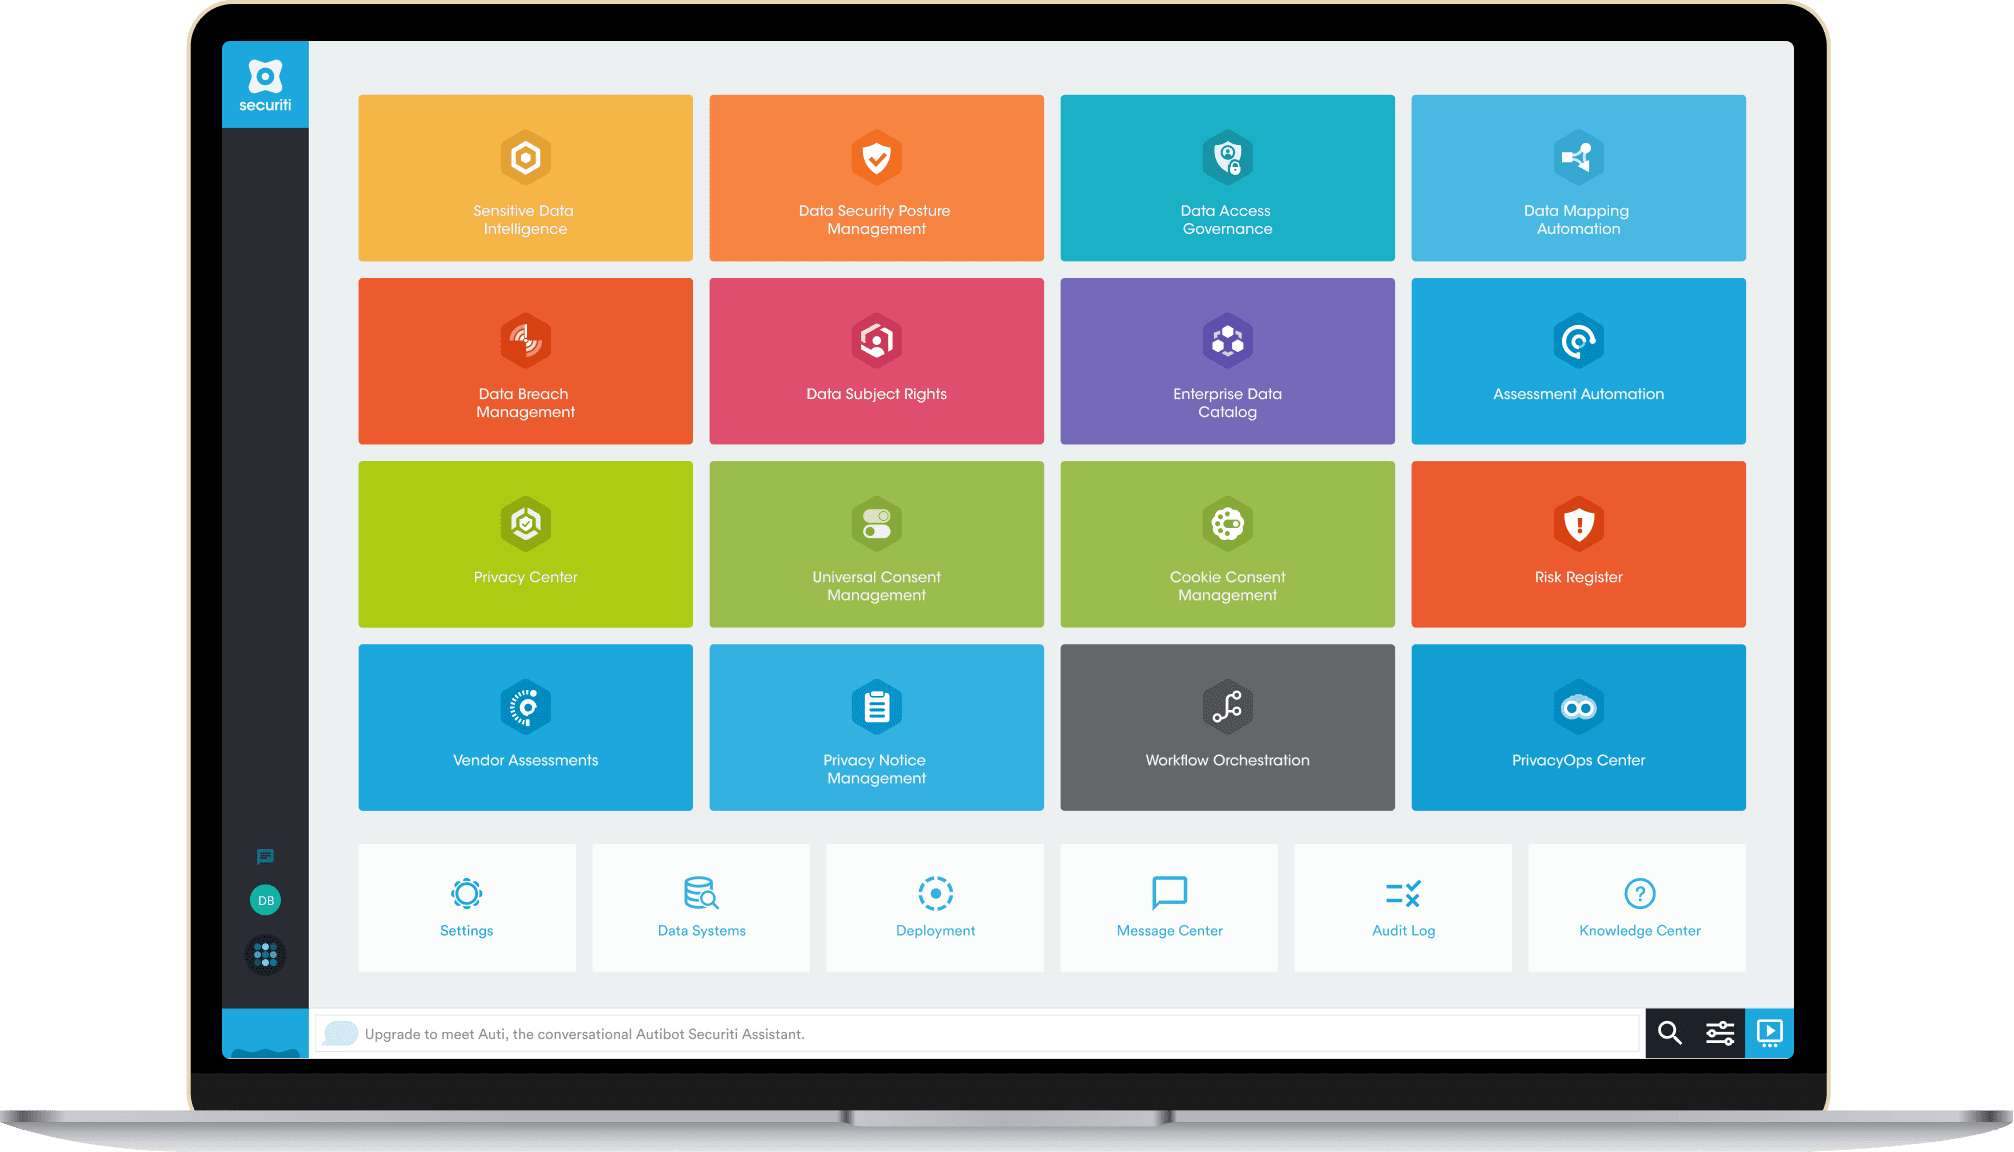
Securiti’s Data Security Posture Management module enables organizations to minimize data breach risk, secure data sharing, and improve data privacy and compliance while reducing the cost and complexity of building data controls. With Securiti’s DSPM, organizations can discover and catalog all data assets, gain contextual data intelligence to classify sensitive data, prioritize and remediate data system misconfigurations based on sensitivity, prevent unauthorized data access, honor individuals' data privacy, govern data controls to prevent sensitive data sprawl and unify data intelligence and controls across cloud environments.

3

Securiti’s Compliance Management automation enables organizations to navigate the ever-intricate landscape of emerging AI and data regulations and streamline compliance by leveraging common controls and tests, a rich library of frameworks and regulations, pre-defined multi-compliance checks, seamless reporting, and Copilot—an LLM-powered chatbot offering insightful guidance.

4

Securiti’s Breach Management provides incident response workflows that help organizations respond to privacy incidents in a timely and effective manner. This is important because, under KSA laws, organizations are required to take reasonable steps to protect personal information from unauthorized access, disclosure, alteration, misuse, or deletion before processing it.

Analyze this article with AI

Prompts open in third-party AI tools.
IDC MarketScape

Securiti named a Leader in the IDC MarketScape for Data Privacy Compliance Software

Read the Report
Videos
View More
Rehan Jalil, Veeam on Agent Commander : theCUBE + NYSE Wired: Cyber Security Leaders
Following Veeam’s acquisition of Securiti, the launch of Agent Commander marks an important step toward helping enterprises adopt AI agents with greater confidence. In...
View More
Mitigating OWASP Top 10 for LLM Applications 2025
Generative AI (GenAI) has transformed how enterprises operate, scale, and grow. There’s an AI application for every purpose, from increasing employee productivity to streamlining...
View More
Top 6 DSPM Use Cases
With the advent of Generative AI (GenAI), data has become more dynamic. New data is generated faster than ever, transmitted to various systems, applications,...
View More
Colorado Privacy Act (CPA)
What is the Colorado Privacy Act? The CPA is a comprehensive privacy law signed on July 7, 2021. It established new standards for personal...
View More
Securiti for Copilot in SaaS
Accelerate Copilot Adoption Securely & Confidently Organizations are eager to adopt Microsoft 365 Copilot for increased productivity and efficiency. However, security concerns like data...
View More
Top 10 Considerations for Safely Using Unstructured Data with GenAI
A staggering 90% of an organization's data is unstructured. This data is rapidly being used to fuel GenAI applications like chatbots and AI search....
View More
Gencore AI: Building Safe, Enterprise-grade AI Systems in Minutes
As enterprises adopt generative AI, data and AI teams face numerous hurdles: securely connecting unstructured and structured data sources, maintaining proper controls and governance,...
View More
Navigating CPRA: Key Insights for Businesses
What is CPRA? The California Privacy Rights Act (CPRA) is California's state legislation aimed at protecting residents' digital privacy. It became effective on January...
View More
Navigating the Shift: Transitioning to PCI DSS v4.0
What is PCI DSS? PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards to ensure safe processing, storage, and...
View More
Securing Data+AI : Playbook for Trust, Risk, and Security Management (TRiSM)
AI's growing security risks have 48% of global CISOs alarmed. Join this keynote to learn about a practical playbook for enabling AI Trust, Risk,...

Spotlight Talks

Spotlight 00:00
AI Agents Unleashed? The Future of Identity & Data Access Security
Watch Now View
Spotlight 00:00
IDC Research: Why Data, AI, Identity and Access Security Must Come Together
Watch Now View
Spotlight 59:11
Data Controls for AI: Findings from the 2026 GigaOm DSPM Research
Watch Now View
Spotlight 1:02:06
Consent by proxy: When AI agents start deciding for us
Watch Now View
Spotlight 1:00:41
Future-Proofing for the Privacy Professional
Watch Now View
Spotlight 50:52
From Data to Deployment: Safeguarding Enterprise AI with Security and Governance
Watch Now View
Spotlight 11:29
Not Hype — Dye & Durham’s Analytics Head Shows What AI at Work Really Looks Like
Watch Now View
Spotlight 11:18
Rewiring Real Estate Finance — How Walker & Dunlop Is Giving Its $135B Portfolio a Data-First Refresh
Watch Now View
Spotlight
Choosing the Right DSPM: An Industry Analyst’s Perspective
Watch Now View
Spotlight 13:38
Accelerating Miracles — How Sanofi is Embedding AI to Significantly Reduce Drug Development Timelines
Sanofi Thumbnail
Watch Now View
Latest
KSA PDPL in 2026 View More
KSA PDPL in 2026: What Organizations Need to Know Now
KSA's Personal Data Protection Law (PDPL) has been fully enforceable since 14th September 2024. Over the past two years, organizations have been navigating overlapping...
EU Digital Sovereignty View More
EU Digital Sovereignty is Moving from Policy to Procurement: What Organizations Need to Know
Digital sovereignty in Europe is moving from policy ambition toward something much more concrete: a framework that can determine how cloud services are assessed,...
View More
What Is Unstructured Data Discovery? A Practical Guide
Unstructured data discovery finds sensitive data in files, chats, and cloud storage. Securiti explains how it works, common challenges, and best practices.
Data Anonymization View More
What Is Data Anonymization
What is data anonymization? Securiti’s latest blog explains how it works, key techniques, and how it differs from pseudonymization. Read to learn more.
Saudi PDPL Compliance Toolkit View More
Saudi PDPL Compliance Toolkit
Turn Saudi PDPL requirements into action with practical checklists, a maturity self-assessment, and a 90-day plan for privacy and compliance leaders.
From Compliance to Continuous Assurance View More
From Compliance to Continuous Assurance: The Next Era of Saudi Data Protection
PDPL compliance didn’t end with the deadline. Learn how to comply with SDAIA enforcement requirements, govern cross-border transfers, and prepare your data for AI.
Data Minimization, Data Minimization for AI, Safe AI, AI Readiness, ROT Data, AI Governance, Data Governance, Data and AI Security, AI Risk Management, Sensitive Data View More
Minimize Before You Scale
Discover why redundant, obsolete, and trivial (ROT) data raises AI-era risks and how to minimize them. Explore practical fixes and business outcomes.
The PDPL Operational Lifecycle View More
The PDPL Operational Lifecycle
Find it. Fix it. Prove it. Repeat. Explore the 10-stage PDPL operational lifecycle, key deadlines, and the evidence regulators expect.
View More
Take the Data Risk Out of AI
Learn how to prepare enterprise data for safe Gemini Enterprise adoption with upstream governance, sensitive data discovery, and pre-index policy controls.
View More
Navigating HITRUST: A Guide to Certification
Securiti's eBook is a practical guide to HITRUST certification, covering everything from choosing i1 vs r2 and scope systems to managing CAPs & planning...
What's
New