New Hampshire Data Privacy Act (NHDPA)

Last Updated on July 31, 2025

Schedule Your
Personal Demo

Learn how you can leverage Securiti’s DataAI Command Platform to address data security, privacy, governance, and compliance.

See a demo
Schedule your demo today

On March 6, 2024, Governor Chris Sununu signed Senate Bill 255, making New Hampshire the 14th U.S. state to enact a comprehensive privacy law, the New Hampshire Data Privacy Act (NHDPA). It became the second state in 2024 to pass such a law, following New Jersey.

 The NHDPA applies to businesses operating in the state or targeting products and services to New Hampshire residents if they meet one of two conditions in a given year: they control or process the personal data of at least 35,000 consumers (excluding data used solely for payment transactions), or they control or process the personal data of at least 10,000 consumers and derive more than 25% of their gross revenue from selling personal data.

The NHDPA is modeled after other state privacy laws, like those in Colorado and California, and grants consumers rights over their personal data, including its collection, processing, and sale. The state's Attorney General enforces the law, which originally included a 60-day cure period for violations. The law came into effect on January 1, 2025. Starting January 1, 2025, the cure period is provided at the attorney general’s discretion, taking into account factors such as the number of violations, nature of processing activities, and the size and complexity of the controller or processor.

The Solution

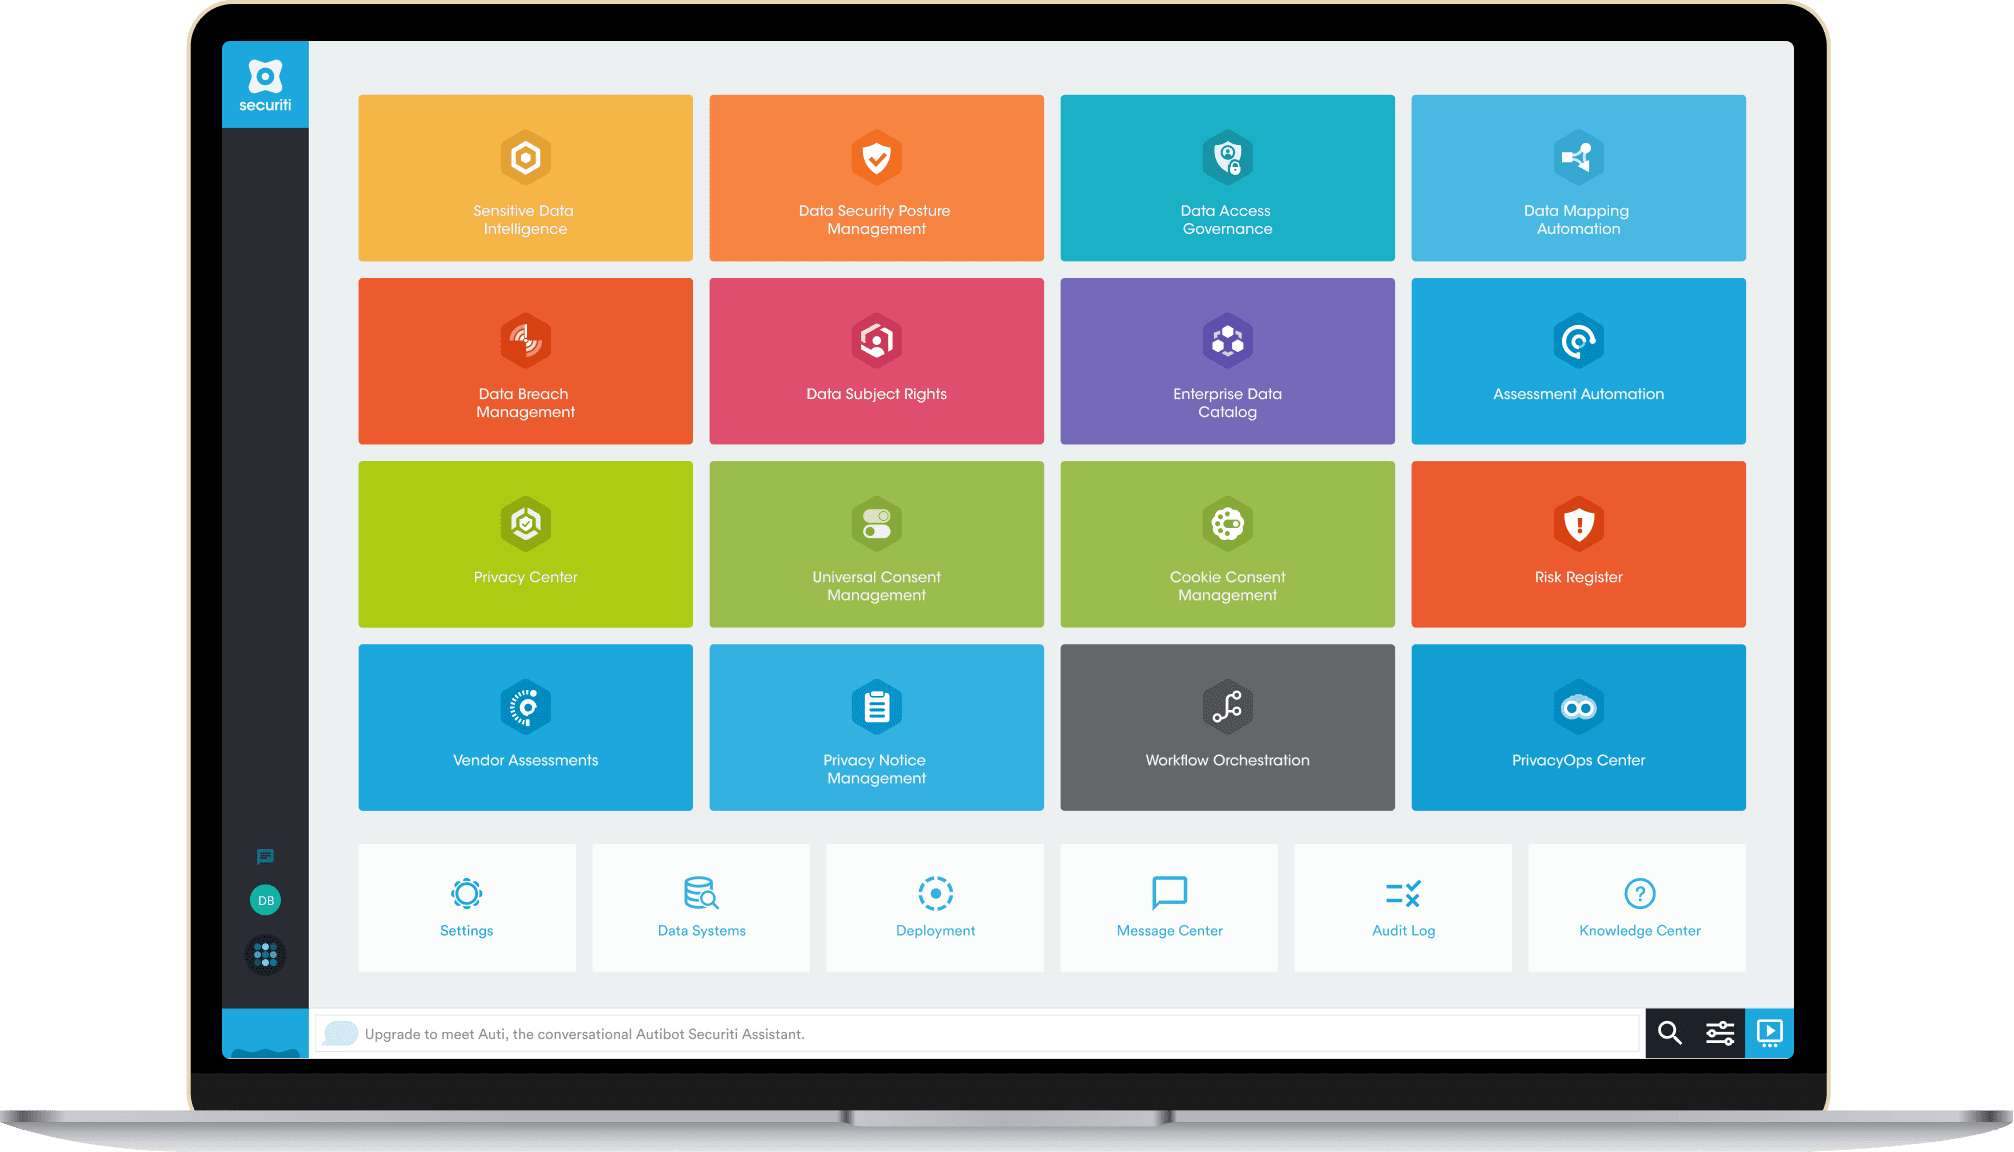
Securiti enables organizations to comply with New Hampshire Data Privacy Act (NHDPA) through AI-driven PI data discovery, DSR automation, documented accountability, enhanced visibility into data processing activities, and AI-driven process automation.

Securiti supports enterprises' journey toward compliance with New Hampshire Data Privacy Act (NHDPA) through automation, enhanced data visibility, and identity linking.

The European Union’s Data Act

Readiness Assessment

NHDPA Provisions

Use our collaborative, multi-regulation, readiness assessment system to measure your organization's posture against NHDPA requirements, identify gaps, and address compliance risks.

Readiness Assessment
Auto Compliance Management

Auto Compliance Management

NHDPA Provisions

Automate compliance with NHDPA using Securiti common controls and tests.

Privacy Notice Management

Section(s): 507-H:6(III)

Automatically update and refresh your privacy policies and notices. Build and publish a privacy notice with pre-built templates, in compliance with the NHDPA.

Privacy Notice Management
Universal Consent Management

Universal Consent Management

Section(s): 507-H:6(I)(b), 507-H:6(I)(d), 507-H:6(I)(f), 507-H:6(I)(g)

Monitor consent for various data processing activities via the central dashboard. Track consent revocation to prevent the processing or transfer of data without consent.

Cookie Consent Management

Section(s): 507-H:6(I)(b), 507-H:6(I)(d), 507-H:6(I)(f), 507-H:6(I)(g)

Scan websites to classify cookies, deploy customized consent collection points, and link consent to user identities and personal data categories collected from end points.

Cookie Consent Management
Sensitive Data Intelligence

Sensitive Data Intelligence

Section(s): 507-H:1(IV), 507-H:1(XX), 507-H:1(IXXVIII)

Discover personal data and sensitive data stored across all systems within the organization and link it to unique data subjects. Visualize personal data sprawl and identify compliance risks.

Data Mapping Automation

Section(s): 507-H:6(III), 507-H:6(I)(a), 507-H:6(I)(b)

Trace data flow across your systems, catalog data collection and transfer, and document business process flows internally and to the processors.

Data Mapping Automation
Data Subject Rights Fulfillments

Data Subject Rights Fulfillments

Section(s): 507-H:4

Create customized web forms and accept verified DSR requests. Automate the initiation of the access, correction, deletion, portability and opt-out request fulfillment workflows in compliance with the NHDPA.

Data Breach Management

Section(s): 507-H:7(I)(b), N.H. Rev. Stat. § 359-C:20

Track and manage potential incidents and data breaches with automated notification guidance based on global regulatory requirements.

Data Breach Management
Data Protection Assessment Automation

Data Protection Assessment Automation

Section(s): 507-H:8(I), 507-H:8(II)

Initiate Data Protection Assessments (DPAs) using compliance templates, invite stakeholders to contribute and review responses, track progress in real-time, and share approved assessments with third parties.

Vendor Assessments

Section(s): 507-H:7(II)(e)

You can track privacy and security readiness from a single interface for all your service providers. You can also collaborate instantly with processors and manage all processor agreements and compliance documents.

Vendor Assessments
Data Security Posture Management

Data Security Posture Management

Section(s): 507-H:6(c)

Discover and auto-remediate security misconfigurations in SaaS and IaaS data systems using a library of rules based on vendor recommendations, industry standards, and best practices.

Key Facts about NHDPA

1

Controllers must obtain consumer consent before collecting or processing additional personal data or using already collected data for purposes beyond those initially communicated or deemed reasonably necessary.

2

Controllers must obtain consumer consent before processing sensitive data or using personal data for purposes beyond what was initially communicated or deemed necessary.

3

Controllers must provide consumers with a reasonably clear and easily accessible privacy notice.

4

Controllers must implement technical, administrative, and organizational security measures to protect personal data from unauthorized access.

5

Controllers must conduct data protection assessments for activities posing heightened risks, such as targeted advertising, data sales, sensitive data processing, and profiling that may lead to harm or deceptive treatment of consumers.

6

The NHDPA gives consumers the right to access, correct, delete, opt-out and data portability.

7

The Attorney General’s Office of New Hampshire (AG) has the exclusive authority to enforce the provisions of the NHDPA.

Analyze this article with AI

Prompts open in third-party AI tools.
IDC MarketScape

Securiti named a Leader in the IDC MarketScape for Data Privacy Compliance Software

Read the Report
Videos
View More
Rehan Jalil, Veeam on Agent Commander : theCUBE + NYSE Wired: Cyber Security Leaders
Following Veeam’s acquisition of Securiti, the launch of Agent Commander marks an important step toward helping enterprises adopt AI agents with greater confidence. In...
View More
Mitigating OWASP Top 10 for LLM Applications 2025
Generative AI (GenAI) has transformed how enterprises operate, scale, and grow. There’s an AI application for every purpose, from increasing employee productivity to streamlining...
View More
Top 6 DSPM Use Cases
With the advent of Generative AI (GenAI), data has become more dynamic. New data is generated faster than ever, transmitted to various systems, applications,...
View More
Colorado Privacy Act (CPA)
What is the Colorado Privacy Act? The CPA is a comprehensive privacy law signed on July 7, 2021. It established new standards for personal...
View More
Securiti for Copilot in SaaS
Accelerate Copilot Adoption Securely & Confidently Organizations are eager to adopt Microsoft 365 Copilot for increased productivity and efficiency. However, security concerns like data...
View More
Top 10 Considerations for Safely Using Unstructured Data with GenAI
A staggering 90% of an organization's data is unstructured. This data is rapidly being used to fuel GenAI applications like chatbots and AI search....
View More
Gencore AI: Building Safe, Enterprise-grade AI Systems in Minutes
As enterprises adopt generative AI, data and AI teams face numerous hurdles: securely connecting unstructured and structured data sources, maintaining proper controls and governance,...
View More
Navigating CPRA: Key Insights for Businesses
What is CPRA? The California Privacy Rights Act (CPRA) is California's state legislation aimed at protecting residents' digital privacy. It became effective on January...
View More
Navigating the Shift: Transitioning to PCI DSS v4.0
What is PCI DSS? PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards to ensure safe processing, storage, and...
View More
Securing Data+AI : Playbook for Trust, Risk, and Security Management (TRiSM)
AI's growing security risks have 48% of global CISOs alarmed. Join this keynote to learn about a practical playbook for enabling AI Trust, Risk,...

Spotlight Talks

Spotlight 00:00
AI Agents Unleashed? The Future of Identity & Data Access Security
Watch Now View
Spotlight 00:00
IDC Research: Why Data, AI, Identity and Access Security Must Come Together
Watch Now View
Spotlight 59:11
Data Controls for AI: Findings from the 2026 GigaOm DSPM Research
Watch Now View
Spotlight 1:02:06
Consent by proxy: When AI agents start deciding for us
Watch Now View
Spotlight 1:00:41
Future-Proofing for the Privacy Professional
Watch Now View
Spotlight 50:52
From Data to Deployment: Safeguarding Enterprise AI with Security and Governance
Watch Now View
Spotlight 11:29
Not Hype — Dye & Durham’s Analytics Head Shows What AI at Work Really Looks Like
Watch Now View
Spotlight 11:18
Rewiring Real Estate Finance — How Walker & Dunlop Is Giving Its $135B Portfolio a Data-First Refresh
Watch Now View
Spotlight
Choosing the Right DSPM: An Industry Analyst’s Perspective
Watch Now View
Spotlight 13:38
Accelerating Miracles — How Sanofi is Embedding AI to Significantly Reduce Drug Development Timelines
Sanofi Thumbnail
Watch Now View
Latest
EU Digital Sovereignty View More
EU Digital Sovereignty is Moving from Policy to Procurement: What Organizations Need to Know
Digital sovereignty in Europe is moving from policy ambition toward something much more concrete: a framework that can determine how cloud services are assessed,...
Australia’s Office of AI: Why Annual Audits Miss What Your AI Can Reach View More
Australia’s Office of AI: Why Annual Audits Miss What Your AI Can Reach
Picture this: a fictional but entirely plausible scenario. An Australian financial institution's AI systems spend six months accessing a customer data repository nobody has...
View More
What Is LLMOps?
LLMOps runs LLMs in production, but most pipelines miss data security. Securiti’s latest blog covers the lifecycle, key risks, and best practices for closing...
Metadata Management View More
What Is Metadata Management? Definition, Benefits & Best Practices
Metadata management is the control plane for enterprise data. Securiti’s latest blog explains how it works, why passive catalogs go stale, and how it...
Saudi PDPL Compliance Toolkit View More
Saudi PDPL Compliance Toolkit
Turn Saudi PDPL requirements into action with practical checklists, a maturity self-assessment, and a 90-day plan for privacy and compliance leaders.
From Compliance to Continuous Assurance View More
From Compliance to Continuous Assurance: The Next Era of Saudi Data Protection
PDPL compliance didn’t end with the deadline. Learn how to comply with SDAIA enforcement requirements, govern cross-border transfers, and prepare your data for AI.
The PDPL Operational Lifecycle View More
The PDPL Operational Lifecycle
Find it. Fix it. Prove it. Repeat. Explore the 10-stage PDPL operational lifecycle, key deadlines, and the evidence regulators expect.
The Toxic Combination Problem in DataAI Risks View More
The Toxic Combination Problem in DataAI Risks
Discover how siloed security alerts create hidden toxic risk combinations and how correlated context helps reduce alert fatigue and uncover compound risks faster.
View More
Take the Data Risk Out of AI
Learn how to prepare enterprise data for safe Gemini Enterprise adoption with upstream governance, sensitive data discovery, and pre-index policy controls.
View More
Navigating HITRUST: A Guide to Certification
Securiti's eBook is a practical guide to HITRUST certification, covering everything from choosing i1 vs r2 and scope systems to managing CAPs & planning...
What's
New