India's Digital Personal Data Protection Act 2023

Operationalize DPDP Compliance with PrivacyOps Platform

Last Updated on June 9, 2026

Schedule Your
Personal Demo

Learn how you can leverage Securiti’s DataAI Command Platform to address data security, privacy, governance, and compliance.

See a demo
Schedule your demo today

The parliament of India has passed the Digital Personal Data Protection Act 2023 (“DPDP Act” or “Act”) on 11th August 2023.

The goal of the DPDP Act is to outline guidelines for processing digital personal data in a way that acknowledges both individuals' rights to privacy protection and the requirement to process personal data for legal purposes.

It provides the rights to data principals (data subjects), outline obligations of data fiduciaries (data handlers/controllers), and furnish penalties for non-compliance. It applies to the processing of digital personal data within India, whether collected online or offline.

DPDP Act has extraterritorial application if the processing is in connection with offering goods or services to data principals within India.

Following the enactment of the Act, the Ministry of Electronics and Information Technology published the Digital Personal Data Protection Rules, 2025 (DPDP Rules), on November 13, 2025. These rules provide the operational framework for the Act, detailing specific procedures for verifiable parental consent, timelines for data erasure, and the registration of Consent Managers to help individuals manage their data permissions. The rules related to the Data Protection Board are already in force, however, consent manager related rules take effect 12 months after finalization in November 2026, with all other obligations applying after 18 months, i.e, May 2027.

The Solution

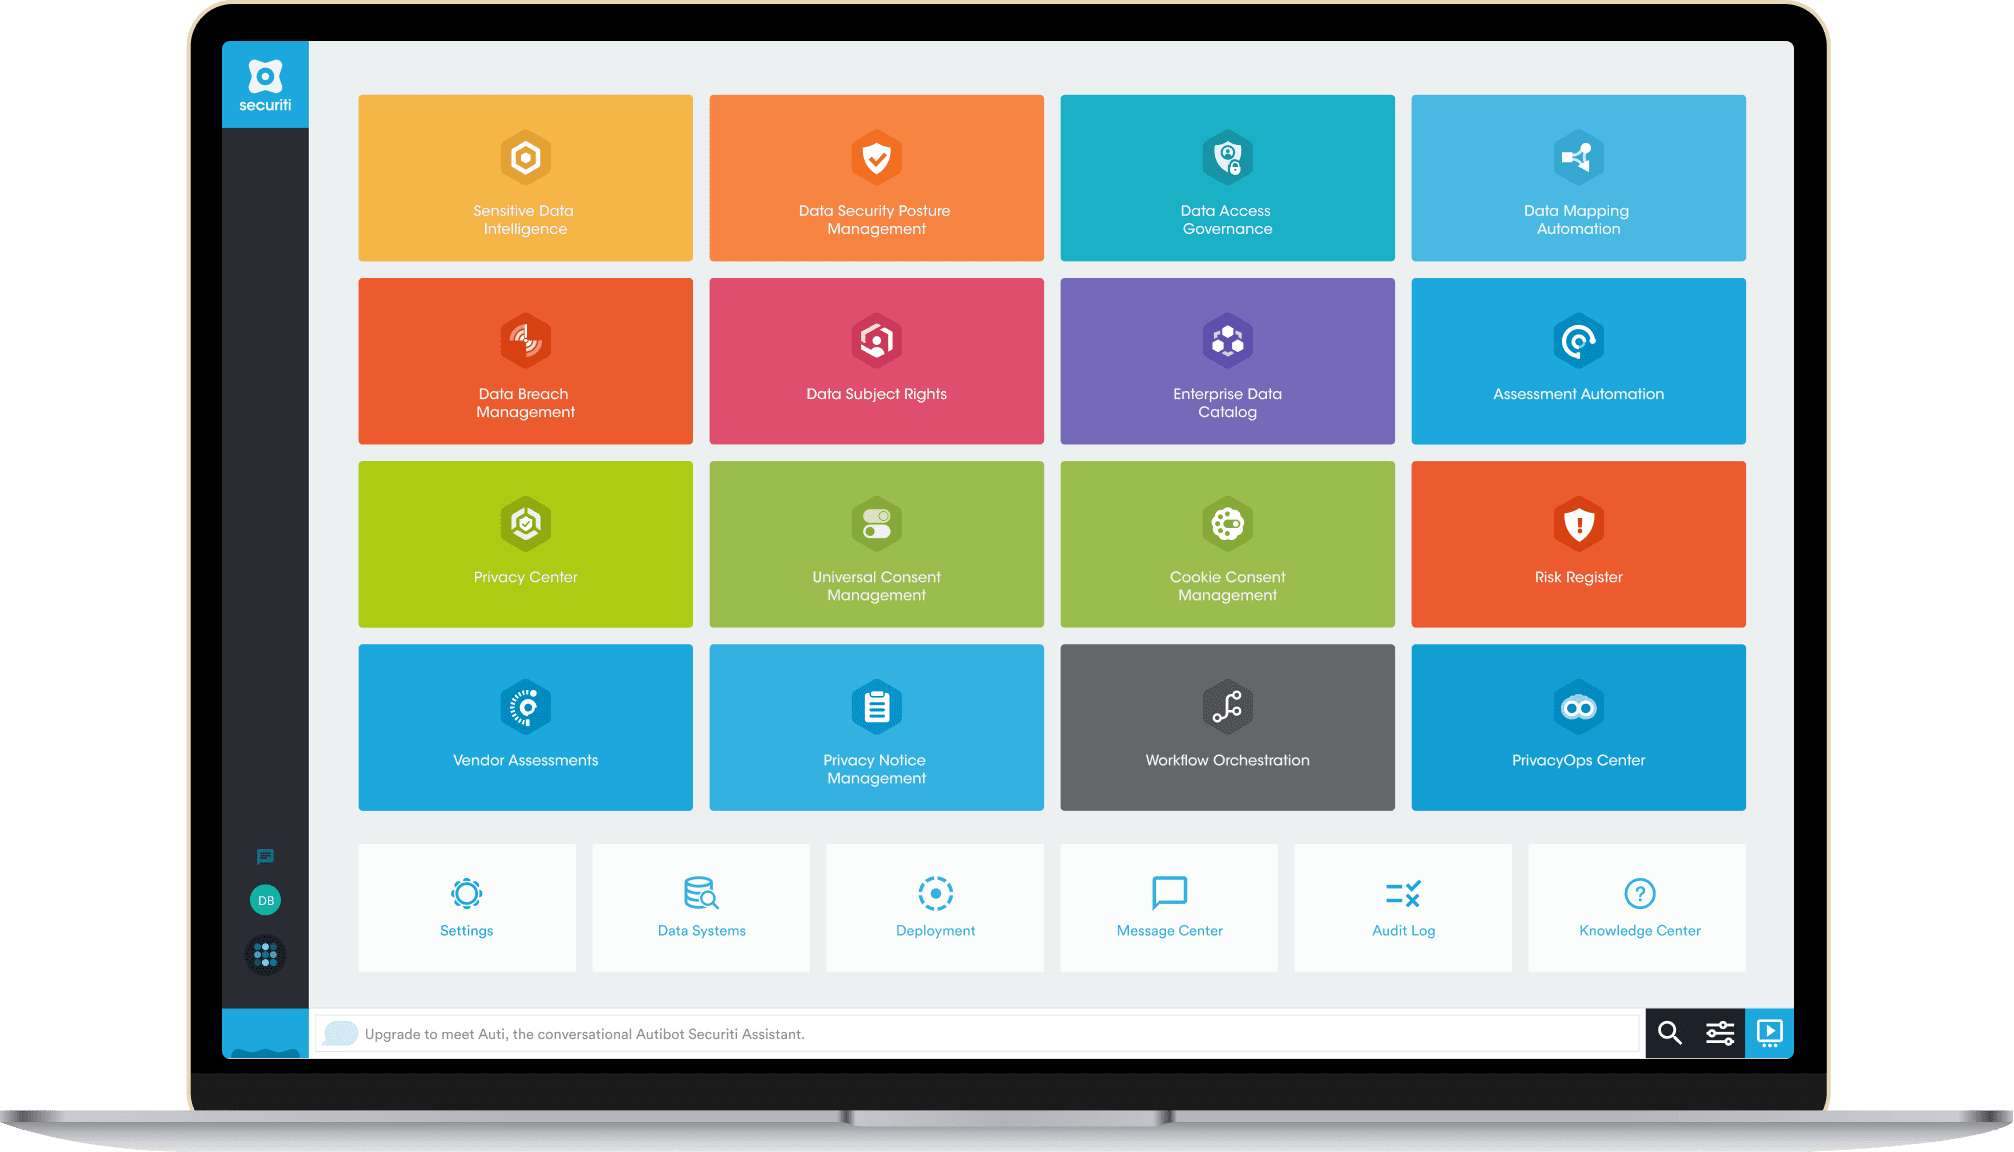
Securiti enables organizations to comply with India's Digital Personal Data Protection Act 2023 through AI-driven PI data discovery, DSR automation, documented accountability, enhanced visibility into data processing activities, and AI-driven process automation.

Securiti supports enterprises in their journey toward compliance with the DPDP Act through automation, enhanced data visibility, and identity linking.
India DPDP Compliance Solution

See how our comprehensive PrivacyOps platform helps you comply with various sections of India's Digital Personal Data Protection Act 2023.

Request a demo today to learn how Securiti can aid you and your organization's compliance efforts.


Automate Consumer Access Requests

DPDP Act Section 5(3); DPDP Rule 14(1) and 14(2)

Data principals need to be notified about their data privacy rights, and organizations are required to simplify the initiation of verified DSR requests. Automating the delivery and generation of secure data access reports will significantly reduce the risk of compliance violations and reduce the workforce required to comply with all requests.

India DPDP consent preference management
India DPDP data rectify request

Automate the Processing of Rectification & Erasure Requests

DPDP Act Section 8(3) and12; DPDP Rule 8(1) and 8(2)

With the help of automated data principal verification workflows across all appearances of a data principal’s personal data, you can seamlessly fulfill all data rectification and erasure requests.

Monitor and Track Consent

DPDP Act Sections 4(1)(a), 6 and 9(1)

Track consent revocation of data principals to prevent the transfer or processing of data without their consent. Seamlessly demonstrate consent compliance to regulators and data principals.

India DPDP consent preference management
India DPDP breach response notification

Assess Third Parties & Manage Vendor Risk

DPDP Act Section 8; DPDP Rule 6(1)(g)

keep track of privacy and security readiness for all your service providers from a single interface. Collaborate instantly with third parties and vendors, automate data requests and deletions, and manage all third parties and vendor contracts and compliance documents.

Map Data Flows and Generate Reports

DPDP Act Section 16; DPDP Rule 13(4) and 23

Track data flows in your organizations, trace this data, catalog, transfer, generate reports, and document business process flows internally and to service providers or third parties.

India DPDP Data Flow Mapping
India DPDP breach response notification

Meet Cookie Compliance

DPDP Act Sections 4(1)(a) and (6); DPDP Rule 3(c)

Automatically scan the web properties within your organization, categorizing tags and cookies. Also, build customizable cookie banners, collect consent, and provide a preference center.

Privacy Policy and Notice Management

DPDP Act Section 5(1); DPDP Rule 3(a) and 3(b)

Automatically update and refresh your privacy policies and notices. Build and publish a privacy notice with pre-built templates.

India DPDP Privacy Policy Management
India DPDP breach response notification

Automate Data Breach Notification

DPDP Act Section 8(6); DPDP Rule 7(1) and 7(2)

Automates compliance actions and breach notifications to concerned stakeholders about security incidents by leveraging a knowledge database on security incident diagnosis and response.

Automate Security Controls

DPDP Act Sections 8(4) and 8(5); DPDP Rule 6(1)

Automate security, privacy, and governance functions with an intuitive workflow orchestration engine. Leverage built-in integrations and customizable triggers to streamline operations, reduce costs and improve accuracy.

India DPDP Security Control Automation
India DPDP Risk Assessments

Automate DPIAs and Risk Assessments

DPDP Act Section 10(2)(c)(i); DPDP Rule 13(1) and 13(2)

Automate DPIA and risk assessments by identifying and reducing the privacy risks posed by new initiatives, procedures, or regulations. DPIA and risk assessments allow organizations to identify privacy risks and mitigate the identified risks.

Rights of a Data Principal Under India's Digital Personal Data Protection Act 2023

Right to Information and Access Personal Data

The data principal has the right to request information from the data fiduciary. This includes obtaining confirmation of whether the data fiduciary is or has processed the data principal's personal data, a summary of the personal data being or that has been processed, and the identities of all data fiduciaries with whom the personal data has been shared, along with the categories of personal data shared.


Right to Correction and Erasure of Personal Data

A data principal shall have the right to correction and erasure of their personal data. Upon receiving a request for such correction of the personal data from a data principal, a data fiduciary is required to correct any inaccuracies, complete any incomplete information and update a data principal's personal data in the systems accordingly. In addition, the data fiduciary must also erase the personal data upon receiving such a request from the data subject unless data retention is required by law.


Right of Grievance Redressal

A data principal has the right to lodge a complaint with a data fiduciary. If a data fiduciary's response to a grievance is unsatisfactory, or if no response is received within the time frame that may be prescribed, the data principal may submit a complaint with the Data Protection Board in the way that may be required.


Right to Nominate

A data principal shall be entitled to designate any other person in the manner that may be prescribed who shall, in the case of the data principal's death or incapacity, exercise the data principal's rights in accordance with the requirements of this Act.

Key Facts Related to India's Digital Personal Data Protection Act 2023

1

The Data Protection Board (DPB) under the DPDP Act serves primarily as an adjudicating body rather than a comprehensive regulatory authority. While it handles grievance adjudication and penalizing data breaches, its scope does not extend to broader regulatory functions such as cross-border data transfer regulation or rulemaking for data fiduciaries' obligations. Instead, these responsibilities remain with the Central Government.

2

Transfer of data outside the territory of India is allowed, however, only after conducting an assessment of relevant factors and defining specifications of terms and conditions for transfers.

3

If a data fiduciary or data processor fails to take reasonable security safeguards to prevent a personal data breach, the penalty imposed would be 250 crore Indian Rupees.

4

The data fiduciary may only engage, appoint, use, or involve a data processor to process personal data on its behalf  under a valid contract.

Analyze this article with AI

Prompts open in third-party AI tools.
IDC MarketScape

Securiti named a Leader in the IDC MarketScape for Data Privacy Compliance Software

Read the Report
Videos
View More
Rehan Jalil, Veeam on Agent Commander : theCUBE + NYSE Wired: Cyber Security Leaders
Following Veeam’s acquisition of Securiti, the launch of Agent Commander marks an important step toward helping enterprises adopt AI agents with greater confidence. In...
View More
Mitigating OWASP Top 10 for LLM Applications 2025
Generative AI (GenAI) has transformed how enterprises operate, scale, and grow. There’s an AI application for every purpose, from increasing employee productivity to streamlining...
View More
Top 6 DSPM Use Cases
With the advent of Generative AI (GenAI), data has become more dynamic. New data is generated faster than ever, transmitted to various systems, applications,...
View More
Colorado Privacy Act (CPA)
What is the Colorado Privacy Act? The CPA is a comprehensive privacy law signed on July 7, 2021. It established new standards for personal...
View More
Securiti for Copilot in SaaS
Accelerate Copilot Adoption Securely & Confidently Organizations are eager to adopt Microsoft 365 Copilot for increased productivity and efficiency. However, security concerns like data...
View More
Top 10 Considerations for Safely Using Unstructured Data with GenAI
A staggering 90% of an organization's data is unstructured. This data is rapidly being used to fuel GenAI applications like chatbots and AI search....
View More
Gencore AI: Building Safe, Enterprise-grade AI Systems in Minutes
As enterprises adopt generative AI, data and AI teams face numerous hurdles: securely connecting unstructured and structured data sources, maintaining proper controls and governance,...
View More
Navigating CPRA: Key Insights for Businesses
What is CPRA? The California Privacy Rights Act (CPRA) is California's state legislation aimed at protecting residents' digital privacy. It became effective on January...
View More
Navigating the Shift: Transitioning to PCI DSS v4.0
What is PCI DSS? PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards to ensure safe processing, storage, and...
View More
Securing Data+AI : Playbook for Trust, Risk, and Security Management (TRiSM)
AI's growing security risks have 48% of global CISOs alarmed. Join this keynote to learn about a practical playbook for enabling AI Trust, Risk,...

Spotlight Talks

Spotlight 59:11
Data Controls for AI: Findings from the 2026 GigaOm DSPM Research
Watch Now View
Spotlight 1:02:06
Consent by proxy: When AI agents start deciding for us
Watch Now View
Spotlight 1:00:41
Future-Proofing for the Privacy Professional
Watch Now View
Spotlight 50:52
From Data to Deployment: Safeguarding Enterprise AI with Security and Governance
Watch Now View
Spotlight 11:29
Not Hype — Dye & Durham’s Analytics Head Shows What AI at Work Really Looks Like
Watch Now View
Spotlight 11:18
Rewiring Real Estate Finance — How Walker & Dunlop Is Giving Its $135B Portfolio a Data-First Refresh
Watch Now View
Spotlight
Choosing the Right DSPM: An Industry Analyst’s Perspective
Watch Now View
Spotlight 13:38
Accelerating Miracles — How Sanofi is Embedding AI to Significantly Reduce Drug Development Timelines
Sanofi Thumbnail
Watch Now View
Spotlight 10:35
There’s Been a Material Shift in the Data Center of Gravity
Watch Now View
Spotlight 14:21
AI Governance Is Much More than Technology Risk Mitigation
Watch Now View
Latest
Australia’s Office of AI: Why Annual Audits Miss What Your AI Can Reach View More
Australia’s Office of AI: Why Annual Audits Miss What Your AI Can Reach
Picture this: a fictional but entirely plausible scenario. An Australian financial institution's AI systems spend six months accessing a customer data repository nobody has...
View More
A Complete DSPM Needs Classification and Context
Classification is one of the core functions a DSPM program handles, and it usually runs in tandem with discovery, since together they form the...
View More
DSPM for AI: Extending Data Posture to Prompts, Pipelines & Agents
Learn how DSPM for AI helps enterprises discover sensitive data, assess exposure, govern access, reduce risk, and secure data before AI systems and agents...
DSPM vs DLP: Key Data Security Differences Explained View More
DSPM vs DLP: Key Data Security Differences Explained
Compare DSPM vs DLP to understand how they differ in data discovery, classification, monitoring, prevention, risk reduction, and protecting sensitive enterprise data.
The Context Layer for Data+AI Security View More
The Context Layer for Data+AI Security
Discover how Securiti’s DataAI Command Graph connects data, identity, cloud, and AI findings to uncover contextual risk and toxic combinations.
View More
Privacy RFP Buyer’s Guide: 120+ Questions to Evaluate Privacy Automation Platforms
Download the Privacy RFP Buyer’s Guide with 120+ practical questions to evaluate privacy automation platforms across compliance, security, integrations, governance, and scalability.
The Toxic Combination Problem in DataAI Risks View More
The Toxic Combination Problem in DataAI Risks
Discover how siloed security alerts create hidden toxic risk combinations and how correlated context helps reduce alert fatigue and uncover compound risks faster.
The Cloud Storage Bill Nobody Reads View More
The Cloud Storage Bill Nobody Reads
Hidden cloud storage costs add up fast. Learn how redundant, obsolete, and trivial data drives unnecessary spend, expands risk, and why automated data minimization...
View More
Take the Data Risk Out of AI
Learn how to prepare enterprise data for safe Gemini Enterprise adoption with upstream governance, sensitive data discovery, and pre-index policy controls.
View More
Navigating HITRUST: A Guide to Certification
Securiti's eBook is a practical guide to HITRUST certification, covering everything from choosing i1 vs r2 and scope systems to managing CAPs & planning...
What's
New