Cookie Text: A Comprehensive Guide

Download: Consent Report Q1 2026
Published February 2, 2022
Contributors

Anas Baig

Product Marketing Manager at Securiti

Maria Khan

Data Privacy Legal Manager at Securiti

FIP, CIPT, CIPM, CIPP/E

Listen to the content

A decade ago, a user would type in the name of their preferred website and begin their browsing. They would note how the more they browsed the site, the better ads they received that directed them towards the exact goods/services they were looking for. This was possible because of cookies. Cookies are small bits of text stored on your browser by the site that help it collect information on your browsing behavior. Naturally, this results in the website showing the user better goods/services based on what they were searching for.

A decade later, the average user journey on a website hasn't changed much, except for one major thing. Depending on where the user was accessing the site, the first thing they would see on the website would be a dialogue box, asking them to Accept or Manage cookies.

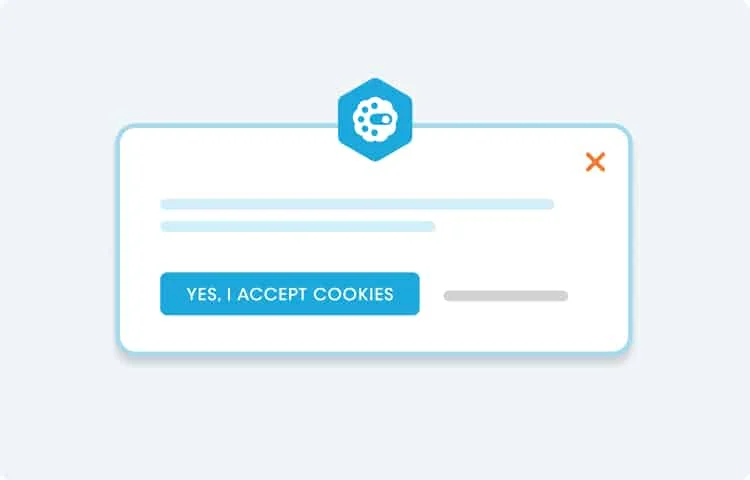
Thanks to GDPR and several other data protection laws, websites cannot store cookies on a user's device by default when catering to EU and UK residents. They need proper and informed consent from the visitor to do so. The text in the dialogue box, where the user will choose to either accept cookies or manage what cookies they want to be stored, is known as Cookie Text.

As surprising as it may seem, this small piece of text is the current standard way a website uses to convince the consumers to accept cookies on their website.

In simple terms, cookie text is the actual text a user will see on the dialogue box when they are presented with the choice to either accept cookies or reject them. While it may not seem like a big deal, a cookie text is essentially the only tool a website has to gain consent from users to store cookies on their site. Given how cookies can help ensure a user sees highly targeted ads that are more likely to convert and help a website identify its users better, it becomes clear just how vital cookie texts are.

The European Data Protection Board's definition states that "valid consent is a freely given, informed, specific and unambiguous indication of a user's wishes. Scrolling and continued browsing on websites is not valid consent, and cookie banners are not allowed to have pre-ticked checkboxes.

Naturally, a website's cookie text should adhere to this definition and seek to elicit consent while guiding users to appropriate resources on the website if they have any further questions on the matter.

Why Websites Use Cookie Texts

Cookie texts are how a website can communicate its exact cookie consent policy. The dialogue box where the cookie text is shown must be precise enough without limiting any information a user must know.

Usually, the cookie text is the first thing a user will see when visiting a website. Unlike the cookie policy statement where a website has to explain what kind of cookies are being used, how the website uses them, what information they store, and how users can manage them, a cookie text is a far more straightforward form of text that greets a user upon arrival to the site and requests their consent to store cookies on their device.

Cookie texts can be thought of as a permission tool as it is the only way a website can make a case for storing cookies on a user's device.

Cookie Text Requirements for GDPR Compliance

The General Data Protection Regulation (GDPR) set the benchmark for data protection laws. The GDPR required all websites using cookies to take robust precautions to ensure their users' data privacy and elicit proper consent before collecting any form of data. This is known as opt-in consent, where a user has to opt-in with express consent to have their data collected.

One of the things that stands out the most about how the GDPR deals with cookies is the fact "cookies" are not mentioned at all within the regulation. Instead, the term used is "personal data identifiers". Most websites use cookies to carry out that exact function, i.e., to store information about a user's age, language, device being used, time zone, country, etc. However, since there are cookies that do not collect personal information but are strictly necessary for a website to function properly, those technologies are exempt from GDPR.

As far as cookie text is concerned, the GDPR deals with how a website is supposed to inform its users about cookies. Any cookie text on any webpage on a website must contain the following information:

  • Information about using cookies and their purpose when users visit the website.
  • How to accept and reject cookies before storing them on a device.
  • Keep cookies (except strictly necessary cookies) blocked until the user gives consent.
  • How users can select what cookies they want the website to store on their device.
  • How users can allow or withdraw cookie consent if necessary.
  • Keep a log of all the user consent.
  • Renew cookie consent every six months (depends on the local data protection authority guidelines).

Cookie Text for CCPA Compliance

The California Consumer Privacy Act (CCPA) has a somewhat different approach towards cookies than the GDPR. While the GDPR follows the opt-in consent model, the CCPA follows the opt-out model. Under the opt-out model, websites have the right to store cookies and collect information on a user by default. A user can only ask a website not to share or sell any data collected on them to a third party. Furthermore, websites are under no obligation to discontinue data collection even after a user requests so.

Under the opt-out model, a website must make it easier for users to opt-out of having their data sold or shared with third parties by making a "Do Not Sell My Personal Information" link clearly available and accessible on every website's webpage. The cookie text for such a Do Not Sell My Personal Information must fulfill the following requirements:

  • Inform the users about cookies, their source, and their purpose.
  • Allow users to opt-out of cookies ("Do Not Sell My Personal Information" link) that sell or share personal information with third parties.
  • Link to privacy or cookie notice that explains what type of cookies the site uses, the source, the data collected, their purpose, and how users can control them.

Cookie Text Examples

Here are some examples of cookie text from various websites from different countries adhering to various data protection laws from across the world:
cookie text
cookie text
cookie text
cookie text

Best Cookie Text Practices

It should be clear by now that there is no "one size fit all" approach when it comes to your cookie text. Owing to the different legal requirements of various data protection laws around the world, it is likely that a website may need to alter its cookie text per country. Or in the case of the US, this alteration in cookie text will be needed on a state level since different states have their own data protection laws.

However, there are some key practices that any website can inculcate in their cookie text wherever they may be operating from to ensure they remain legally compliant without making things more complicated than they need to be.

  • Use simple & easily understandable language
  • Avoid jargon and technical or legal terms
  • Give users an equal opportunity to opt-in or out without restricting their browsing experience
  • Explain exactly what kind of cookies you use
  • Explain what information you share/sell to third parties and how users can opt-out of it

How Securiti Can Help

Cookie consent management has taken an unprecedented level of importance in 2022. Several data protection laws are being enacted worldwide that mandate all websites ensure their users are adequately informed and educated about their digital privacy rights. Businesses have to figure out how they can continue trying to optimize their users' browsing experience without breaching any consent requirements.

A robust and instantly adaptable cookie consent management system is the key to achieving that goal. And such a robust and instantly adaptable cookie consent management system can only be achieved via automation. Owing to the sheer amount of data involved, it makes sense for businesses to automate this vital process to ensure effectiveness and efficiency.

Securiti is a market leader in providing AI and machine-learning-based enterprise solutions to various data compliance-related problems such as cookie consent management.

Request a demo today to see Securiti's tools in action and learn how Securiti can help your business.


Frequently Asked Questions (FAQs)

A cookie text  is the actual text a user will see on the dialogue box when they are presented with the choice to either accept cookies or reject them.

Cookies usage text is the content within a cookie notice that informs users about the website's use of cookies. It typically covers the types of cookies,how the website uses them, what information they store and how users can manage their preferences.

The cookie text is a concise message that users see upon visiting a website, requesting their consent to store cookies. In contrast, the cookie notice provides detailed information about the types of cookies used, their functions, and user management options.

Schedule Your
Personal Demo

Learn how you can leverage Securiti’s DataAI Command Platform to address data security, privacy, governance, and compliance.

See a demo
Schedule your demo today

Analyze this article with AI

Prompts open in third-party AI tools.
Join Our Newsletter

Get all the latest information, law updates and more delivered to your inbox


More Stories that May Interest You

Take a
Product Tour

See how easy it is to manage privacy compliance with robotic automation.

Videos
View More
Rehan Jalil, Veeam on Agent Commander : theCUBE + NYSE Wired: Cyber Security Leaders
Following Veeam’s acquisition of Securiti, the launch of Agent Commander marks an important step toward helping enterprises adopt AI agents with greater confidence. In...
View More
Mitigating OWASP Top 10 for LLM Applications 2025
Generative AI (GenAI) has transformed how enterprises operate, scale, and grow. There’s an AI application for every purpose, from increasing employee productivity to streamlining...
View More
Top 6 DSPM Use Cases
With the advent of Generative AI (GenAI), data has become more dynamic. New data is generated faster than ever, transmitted to various systems, applications,...
View More
Colorado Privacy Act (CPA)
What is the Colorado Privacy Act? The CPA is a comprehensive privacy law signed on July 7, 2021. It established new standards for personal...
View More
Securiti for Copilot in SaaS
Accelerate Copilot Adoption Securely & Confidently Organizations are eager to adopt Microsoft 365 Copilot for increased productivity and efficiency. However, security concerns like data...
View More
Top 10 Considerations for Safely Using Unstructured Data with GenAI
A staggering 90% of an organization's data is unstructured. This data is rapidly being used to fuel GenAI applications like chatbots and AI search....
View More
Gencore AI: Building Safe, Enterprise-grade AI Systems in Minutes
As enterprises adopt generative AI, data and AI teams face numerous hurdles: securely connecting unstructured and structured data sources, maintaining proper controls and governance,...
View More
Navigating CPRA: Key Insights for Businesses
What is CPRA? The California Privacy Rights Act (CPRA) is California's state legislation aimed at protecting residents' digital privacy. It became effective on January...
View More
Navigating the Shift: Transitioning to PCI DSS v4.0
What is PCI DSS? PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards to ensure safe processing, storage, and...
View More
Securing Data+AI : Playbook for Trust, Risk, and Security Management (TRiSM)
AI's growing security risks have 48% of global CISOs alarmed. Join this keynote to learn about a practical playbook for enabling AI Trust, Risk,...

Spotlight Talks

Spotlight 00:00
AI Agents Unleashed? The Future of Identity & Data Access Security
Watch Now View
Spotlight 00:00
IDC Research: Why Data, AI, Identity and Access Security Must Come Together
Watch Now View
Spotlight 59:11
Data Controls for AI: Findings from the 2026 GigaOm DSPM Research
Watch Now View
Spotlight 1:02:06
Consent by proxy: When AI agents start deciding for us
Watch Now View
Spotlight 1:00:41
Future-Proofing for the Privacy Professional
Watch Now View
Spotlight 50:52
From Data to Deployment: Safeguarding Enterprise AI with Security and Governance
Watch Now View
Spotlight 11:29
Not Hype — Dye & Durham’s Analytics Head Shows What AI at Work Really Looks Like
Watch Now View
Spotlight 11:18
Rewiring Real Estate Finance — How Walker & Dunlop Is Giving Its $135B Portfolio a Data-First Refresh
Watch Now View
Spotlight
Choosing the Right DSPM: An Industry Analyst’s Perspective
Watch Now View
Spotlight 13:38
Accelerating Miracles — How Sanofi is Embedding AI to Significantly Reduce Drug Development Timelines
Sanofi Thumbnail
Watch Now View
Latest
KSA PDPL in 2026 View More
KSA PDPL in 2026: What Organizations Need to Know Now
KSA's Personal Data Protection Law (PDPL) has been fully enforceable since 14th September 2024. Over the past two years, organizations have been navigating overlapping...
EU Digital Sovereignty View More
EU Digital Sovereignty is Moving from Policy to Procurement: What Organizations Need to Know
Digital sovereignty in Europe is moving from policy ambition toward something much more concrete: a framework that can determine how cloud services are assessed,...
View More
What Is Unstructured Data Discovery? A Practical Guide
Unstructured data discovery finds sensitive data in files, chats, and cloud storage. Securiti explains how it works, common challenges, and best practices.
Data Anonymization View More
What Is Data Anonymization
What is data anonymization? Securiti’s latest blog explains how it works, key techniques, and how it differs from pseudonymization. Read to learn more.
Saudi PDPL Compliance Toolkit View More
Saudi PDPL Compliance Toolkit
Turn Saudi PDPL requirements into action with practical checklists, a maturity self-assessment, and a 90-day plan for privacy and compliance leaders.
From Compliance to Continuous Assurance View More
From Compliance to Continuous Assurance: The Next Era of Saudi Data Protection
PDPL compliance didn’t end with the deadline. Learn how to comply with SDAIA enforcement requirements, govern cross-border transfers, and prepare your data for AI.
Data Minimization, Data Minimization for AI, Safe AI, AI Readiness, ROT Data, AI Governance, Data Governance, Data and AI Security, AI Risk Management, Sensitive Data View More
Minimize Before You Scale
Discover why redundant, obsolete, and trivial (ROT) data raises AI-era risks and how to minimize them. Explore practical fixes and business outcomes.
The PDPL Operational Lifecycle View More
The PDPL Operational Lifecycle
Find it. Fix it. Prove it. Repeat. Explore the 10-stage PDPL operational lifecycle, key deadlines, and the evidence regulators expect.
View More
Take the Data Risk Out of AI
Learn how to prepare enterprise data for safe Gemini Enterprise adoption with upstream governance, sensitive data discovery, and pre-index policy controls.
View More
Navigating HITRUST: A Guide to Certification
Securiti's eBook is a practical guide to HITRUST certification, covering everything from choosing i1 vs r2 and scope systems to managing CAPs & planning...
What's
New